UK-based · penetration testing & red team operations
[email protected] Forefront IT Security Services
Get AETOS
↓
Your Virtual Cyber Security Team
Most organisations have an IT team. Few have a cyber security team.
Your IT provider keeps the systems running. We keep them secure. Get a whole security team on tap through one Security Front Door: testing, advice and assurance on a pool of days you use as you need, billed monthly, with none of the cost of hiring in-house.
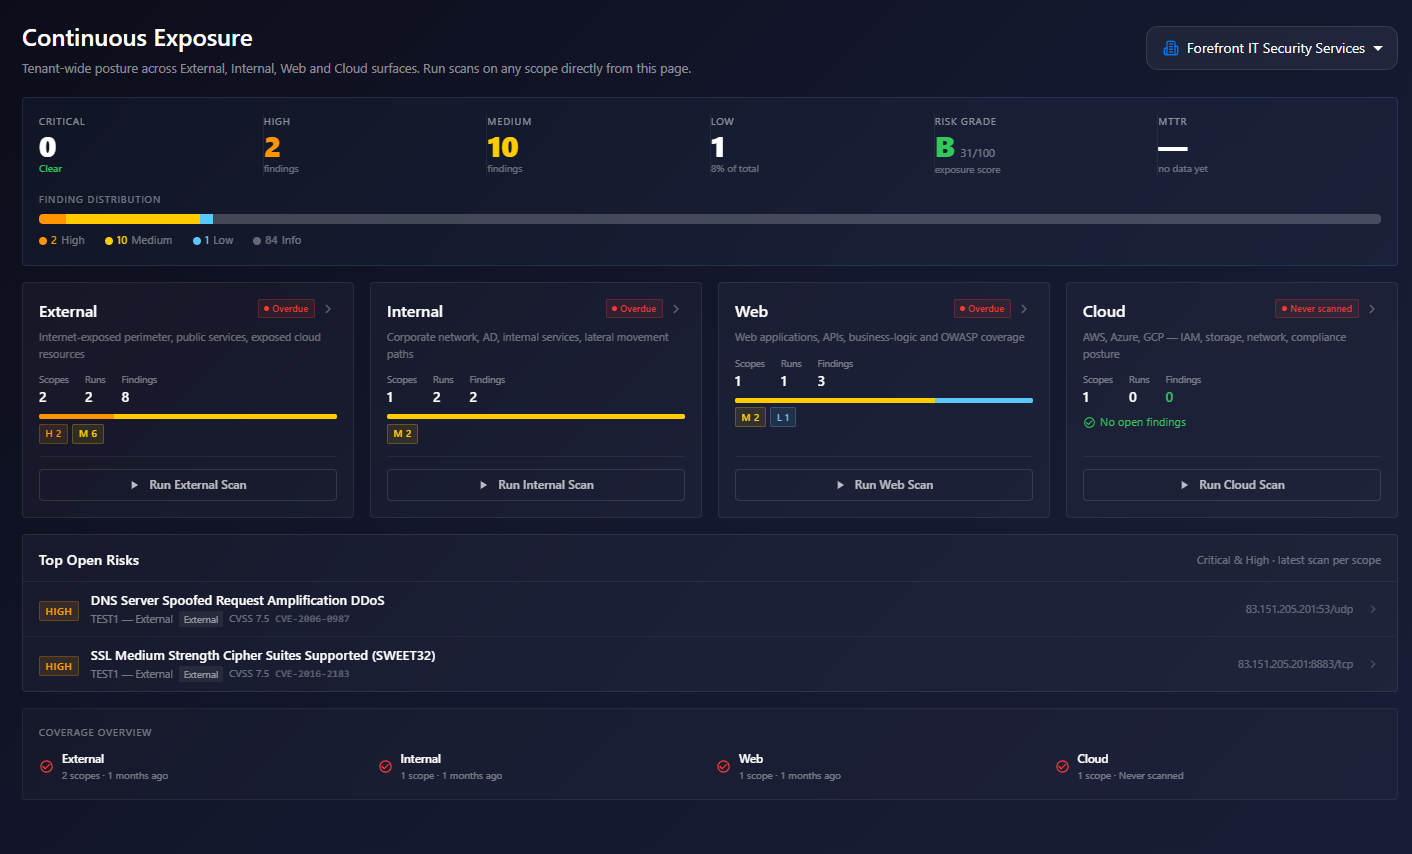
DETECTION GAPS
11
+3 new
Comprehensive Security Testing & Assurance
Clear, expert-led services that show you exactly where you're exposed, and how to fix it.
Penetration Testing
CREST-aligned testing across web applications, internal and external networks, APIs, mobile and cloud, uncovering exploitable vulnerabilities before attackers do.
Red & Purple Teaming
Goal-based adversary simulation and collaborative purple teaming that test your detection, response and resilience against real-world attacker techniques.
Continuous Vulnerability Assessment
Regular, validated scanning that keeps eyes on your attack surface between penetration tests, so new vulnerabilities are caught as they appear, not months later.
Cloud Security Reviews
Cloud security testing for Microsoft 365, Azure and AWS, going beyond a CIS benchmark scan to actively exploit the identity, privilege-escalation and CI/CD paths a real attacker would use.
Cyber Essentials & CE+
Certification readiness and assessment for Cyber Essentials and Cyber Essentials Plus, helping you meet UK compliance and supply-chain requirements.
Security Consultancy
Expert-led advisory, secure architecture review and virtual security resource to strengthen your security programme year-round.
It's not the finding, it's the "so what?"
Anyone can run a scanner. We train every consultant to prove each finding by hand, chain it into real impact, and build the risk picture your board understands, then AETOS keeps proving your defences still see the attack.
Manually Verified
Every finding is proven by hand with a proof-of-concept where possible, not a scanner export dressed up as a report.
So What?
For each vulnerability we establish the real-world consequence: what it actually lets an attacker do, rather than a raw CVSS score.
Chained Into Impact
Individually low findings are chained into a viable attack path that reaches what matters, framed as business risk your board understands.
Proven by AETOS
AETOS then continuously replays those techniques, proving your defences still detect them long after we leave.
Security is a loop, not a line
The assessment is the journey; the report is the deliverable. Each engagement feeds the next, and AETOS wraps the whole thing in continuous, detection-gap-driven exposure management.
Secure the build
Penetration Testing
Hone in on a specific tech stack and embed security into your DevSecOps pipeline, proving what a real attacker could reach.
Widen the lens
Red & Purple Team
Stretch beyond technology to the people and process of the whole business, testing detection and response rather than controls alone.
Never stop
AETOS · CTEM
Detection-gap analysis mapped to MITRE ATT&CK, wrapped in continuous Threat Exposure Management that proves your defences still hold.
A continuous Threat Exposure Management (CTEM) loop, never a one-off test
The Deliverable
Reports that earn their keep
The assessment is the journey, but the report, and any other artifacts you need, is what you keep. Ours are built for real quality and return: clear risk your board reads, reproducible evidence your engineers act on, and prioritised remediation that actually moves the needle.
Security shouldn't end with a penetration test
A penetration test gives you a point-in-time view. Testing from one supplier, Cyber Essentials from another, architecture advice from a contractor, vulnerability scanning from a tool nobody properly reviews. The problem is not the number of suppliers: it is that nobody connects the findings or drives the improvement between one engagement and the next.
Forefront connects the picture.
01 Understand
Where are we exposed?
Establish the real security position before producing findings: what exists, what it connects to, and what is already known about it.
Attack Surface Assessment
Vulnerability Management
CTEM
Architecture Review
Cloud Security Review
Security Baseline
02 Test
What can actually be exploited?
Offensive security against the real environment. Weaknesses proven by hand and chained into the paths an attacker would actually take.
Penetration Testing
Red Teaming
Web Application Testing
API Testing
Infrastructure Testing
Social Engineering
03 Improve
What should we fix first?
Technical evidence turned into something your team can act on, sequenced by what reduces risk rather than by severity label.
Remediation Prioritisation
Security Architecture
Technical Security Advice
Security Roadmaps
Supplier Assurance
Cyber Essentials / CE Plus
04 Validate
Did it actually work?
The improvements tested again, and the controls that should have caught the attack tested against the attack itself.
Retesting
Purple Teaming
Detection Validation
Continuous Validation
Control Validation
AETOS
We don't just tell you what good security should look like. We test whether it actually works.
Forefront is not a governance consultancy that also mentions testing. Offensive security is where we came from, and it is what makes the advice worth having.
The Security Front Door
You're not buying days. You're buying a secure company.
Every Virtual Security Team plan runs through one Security Front Door. Ask, and it gets done: scoped, scheduled, delivered and retested, all tracked in one place. Days are simply how we plan the work. What you are really buying is the outcome.
Free security chats
Got a question? Ask it. A quick check, a second opinion, "should we be worried about this?". Free, and never taken from your days.
No fuss, no chasing
Request it through the Security Front Door and consider it handled. No new quotes, no procurement cycle, no chasing emails.
Cyber Essentials and CE Plus, sorted
Certification whenever you need it, through a licensed IASME Certification Body, with the assessment fees included. No extra invoice: it simply uses a day or two from your plan for a small business, a little more for larger estates.
Training people remember
Security awareness that beats the 30-minute video. Live, tailored sessions built around your people, your systems and the attacks that actually target you.
Through one front door
Certification and compliance
Test and assess
Find and fix
Lead and prepare
AI and apps
Train and develop
The "so what?"
Cloud first does not mean secure
Moving to Microsoft 365 moves the risk. It does not remove it. So we follow the "so what?" the way an attacker would:
Endpoint testing
What can somebody do from one compromised laptop?
Configuration reviews
Microsoft 365, Entra ID and device management, checked against how attackers actually abuse them.
Cloud testing
Somebody gets in through a phishing email or a stolen session. How far can they go, and would you notice?
Buying direct
One plan, one front door, and the peace of mind that your security is covered. No hidden costs, no surprises.
MSPs and IT providers
Same plan, same price, one big difference: spend your days on your own customers and bill them your way. Your client relationship stays yours.
Already a Forefront customer? Sign in to the Security Front Door
Buy a test, or gain a security team
Most organisations do not need a penetration test once a year. They need somebody security-focused to ask whenever something comes up, and capacity ready when it does. Three ways to work with us, from a single project to a full virtual cyber security team.
Project
Penetration Test
One assessment, one scope, one price. The right answer when you have a specific system to test or a certification deadline to hit.
Fixed scope and fixed price
CREST-aligned methodology
Board-ready report and technical evidence
Remediation guidance included
Call-off
Testing Agreement
Commit to a block of penetration testing days for the year and draw them down as you need them. No re-scoping, no re-procuring, every time.
An agreed block of pentest days, on request
Preferential day rate
Priority in the testing calendar
Penetration testing only. Want certification and advice too? That is the Virtual Security Team
Partnership
Virtual Security Team
three tiers, from £1,500 / month
A whole security team on tap, not a series of projects. A pool of days for anything, plus the portal, FISS, advisory and a security roadmap, all through one front door.
An annual pool of days, usable on anything
Ask a security question any time, free
Security Front Door portal and FISS assistant
Baseline, roadmap and regular reviews
Choose your tier
The Virtual Security Team comes in three sizes. Each is a monthly subscription that includes a set number of consultancy days a year, spent on any service, plus the ongoing Security Front Door service with the portal and FISS. A pool day is a day, whatever the work: adversary simulation draws exactly like everything else.
Team
18 days a year
from £1,500 / month
For organisations with no internal security capability who need one they can reach.
Days spent on any service, adversary simulation included
Top-up days available below your committed rate
Managed Exposure (CTEM) via AETOS available as an add-on
Unused days carry into the next year, up to 7
Partner
40 days a year
from £3,000 / month
For organisations under real compliance or customer pressure, with an active roadmap.
Days spent on any service, adversary simulation included
A better effective day rate, and cheaper top-ups
Reviews every six weeks rather than quarterly
Unused days carry into the next year, up to 12
Embedded
72 days a year
from £5,000 / month
For organisations where Forefront is effectively the security function.
Days spent on any service, adversary simulation included
Our best day rate, and the cheapest top-ups
Managed Exposure (CTEM) via AETOS included for a small estate
Priority response, and up to 18 days carried over
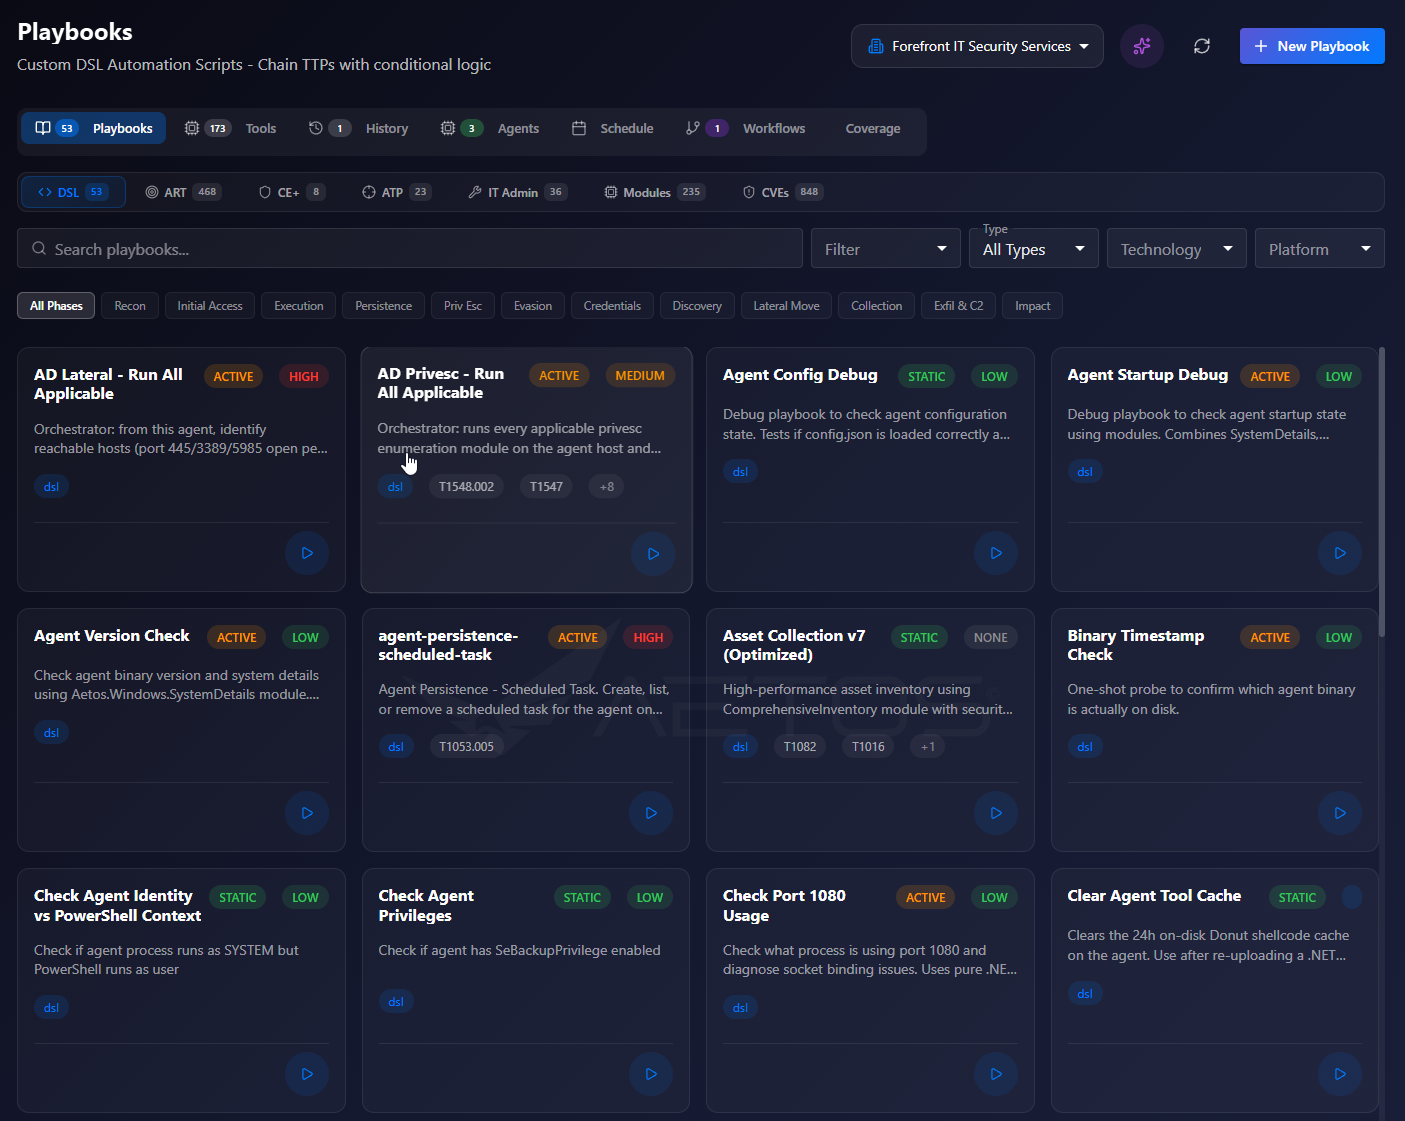
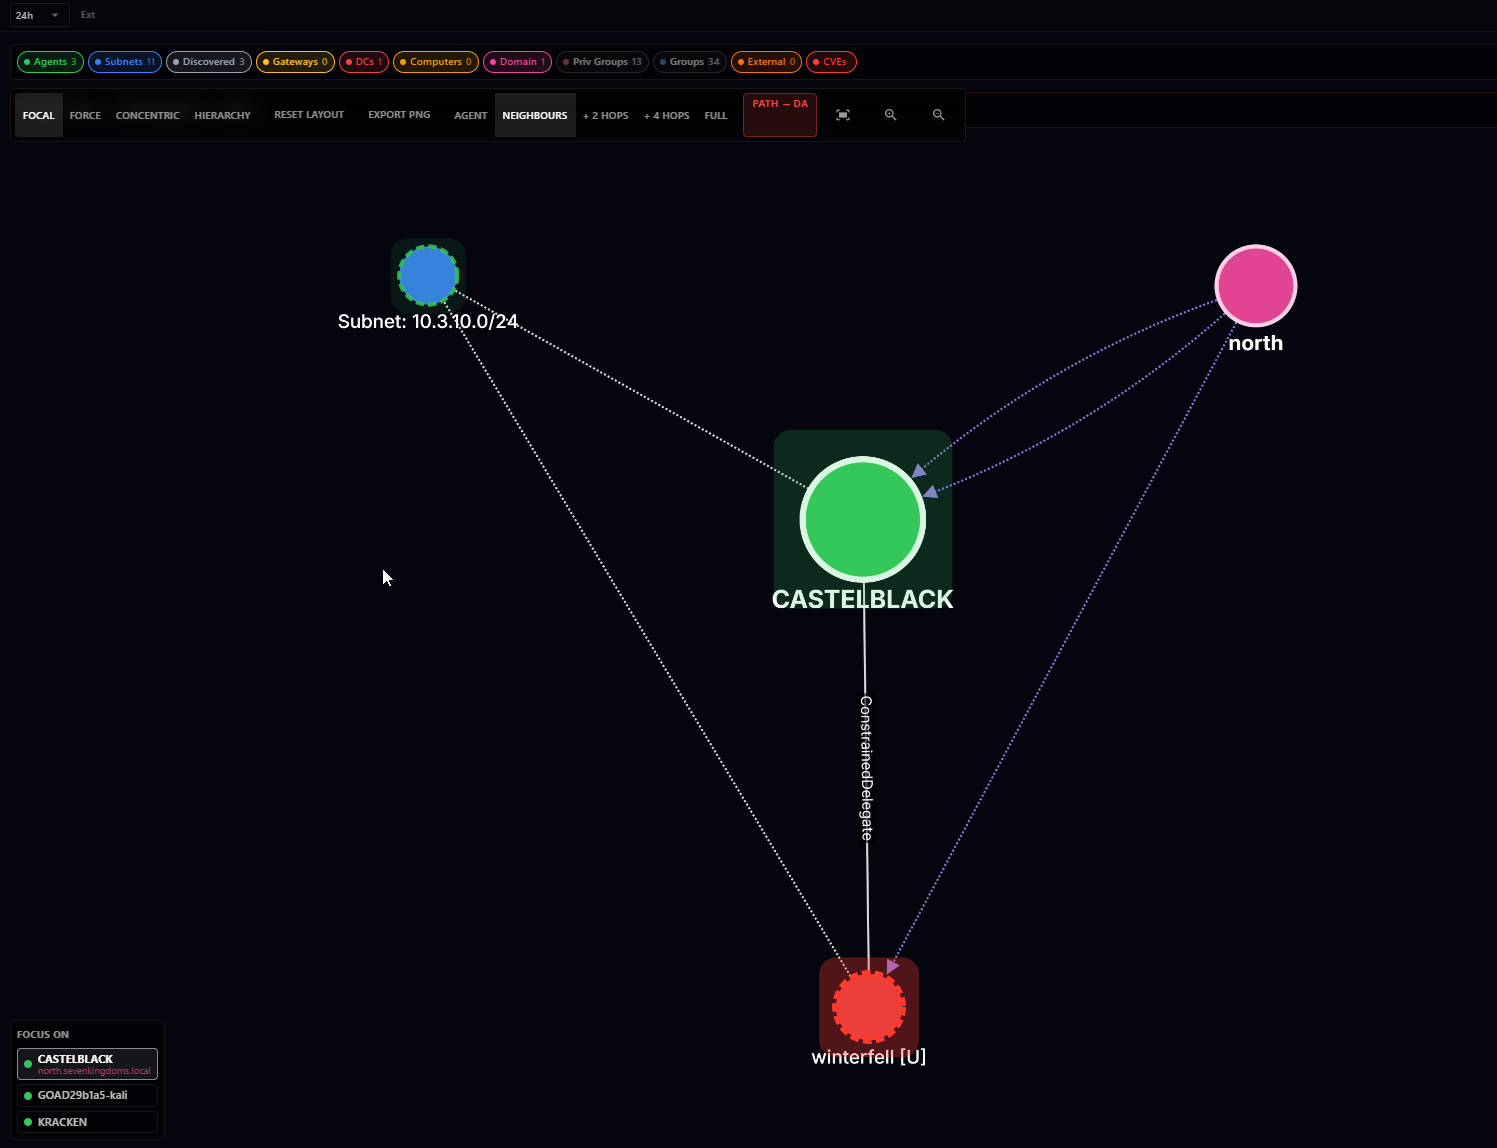
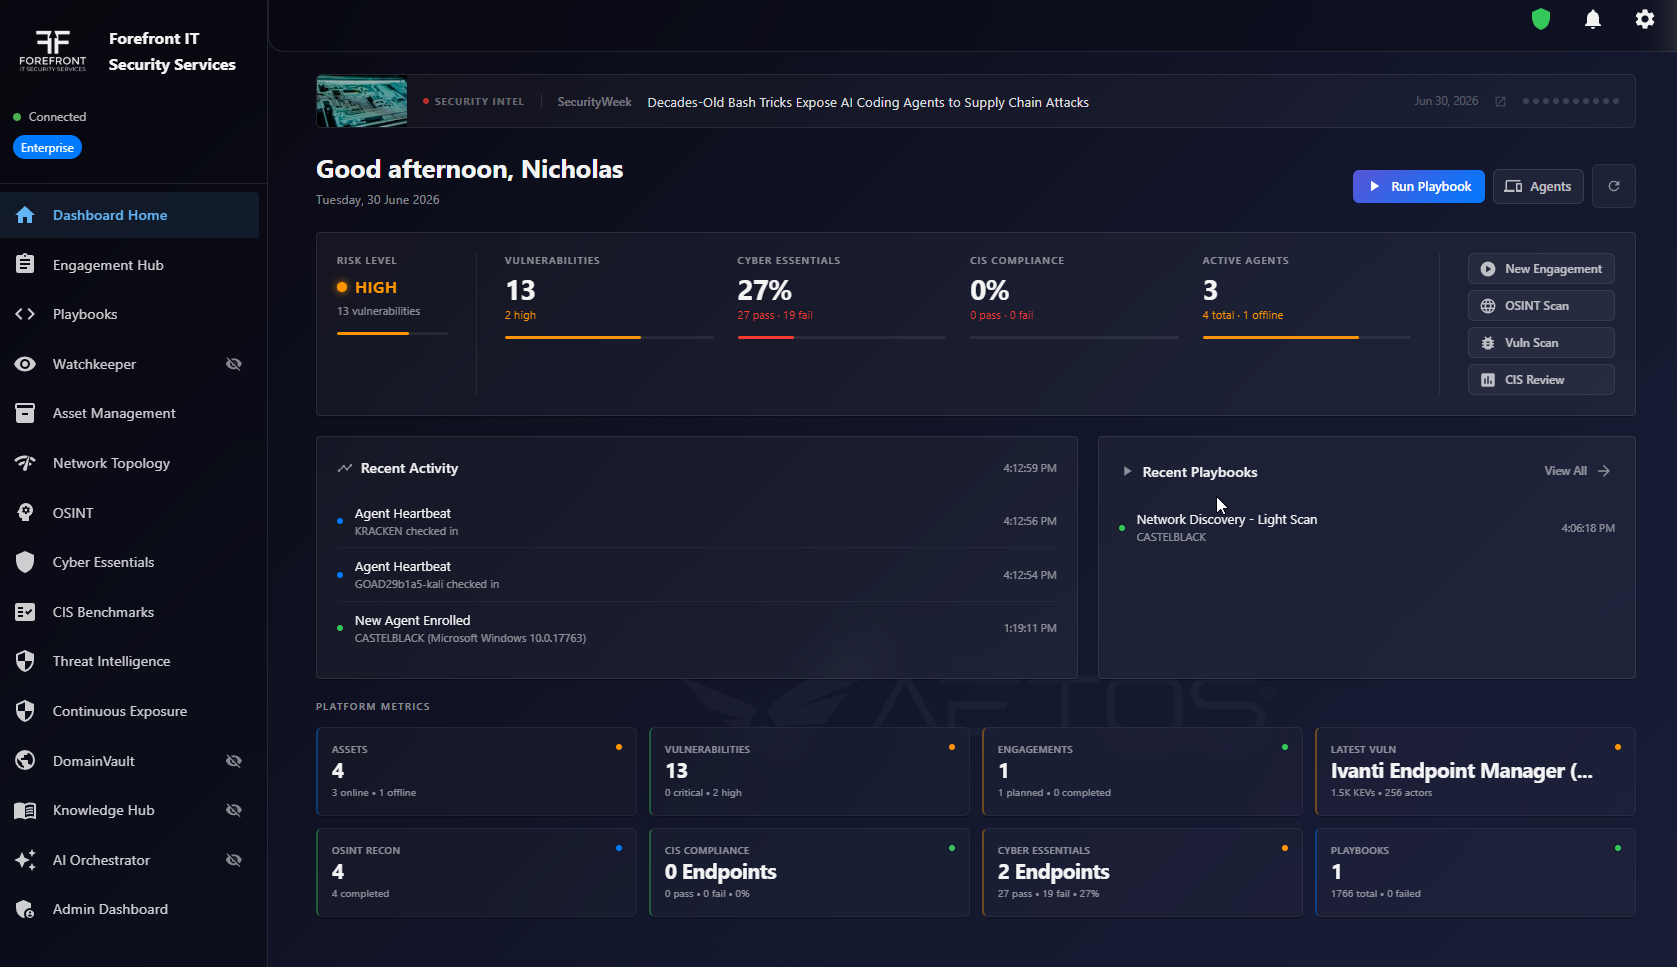
Continuous Validation, Beyond the Test
Forefront supplies AETOS, a platform that safely replays real attacker techniques against your live SIEM to expose the detection gaps that leave you blind, including the stealthy in-memory attacks an EDR misses while it happily flags mimikatz.exe. It doesn't just find the gap, it hands your SOC the tuned rule to close it, then dry-runs that rule against your own data so it won't bury you in false positives. A penetration test is a moment in time; AETOS keeps going.
Adversarial Exposure Validation, real attacker techniques replayed against your live defences
Detection-gap analysis mapped to MITRE ATT&CK, including in-memory techniques that spawn no process
A tuned detection rule for every gap, dry-run against your own data so it will not flood your SOC
External Attack Surface Mapping (EASM), see what attackers see
Unifies findings from your scanners and ours, plus cloud security posture in one place
Continuous Threat Exposure Management (CTEM) with prioritised, evidence-backed remediation
AETOS integrates with your security stack
Splunk
Microsoft 365
Tenable
Qualys
Nessus
Jira
Microsoft Entra
Elastic
Splunk
Microsoft 365
Tenable
Qualys
Nessus
Jira
Microsoft Entra
Elastic
What Sets Us Apart
Hands-On UK Consultants
You get named, UK-based consultants. OSCP, CRTO and Cyber Scheme Team Leader qualified, CE+ Lead Auditors, hands-on offensive testers who prove impact rather than an anonymous offshore scan farm.
Manual-Led, Not Just Scans
Consultants exploit and chain weaknesses by hand to prove real business impact, not the false positives a scanner spits out.
Reporting You Can Act On
Findings rated by real-world risk, with reproduction steps and prioritised fixes, a summary your board reads, depth your engineers action.
Assurance That Continues
A pentest is a moment in time; AETOS keeps validating your live defences between engagements, not a one-off PDF on a shelf.
Trusted Across Regulated Industries
We work with organisations that can't afford to get security wrong, delivering testing that stands up to regulators, auditors and real-world attackers.
Financial Services
Government & Public Sector
Healthcare
Legal
Retail & eCommerce
Technology & SaaS
Industry-Recognised Credentials
Trusted to get it right
Rated 4.9 / 5 by our clients
“The report was the first one our engineers could action without a translation layer, clear, prioritised, and the free retest confirmed every fix.”
Head of IT, Professional Services
“They tested the way a real attacker would and proved the impact, instead of handing us a list of theoretical issues. Genuinely useful.”
IT Director, Financial Services
“Scoping was painless and the proposal was fixed up front, no surprises, and the portal kept findings and remediation in one place.”
Operations Manager, Healthcare
Ready to Strengthen Your Security?
Talk to our security experts about your exposure, and get a clear, prioritised plan to reduce it.